
MobileHackingLabs iOS Challenges
My write-ups for the MobileHackingLabs iOS challenges: reverse engineering the apps, hooking with Frida, bypassing anti-debug and jailbreak checks, and pulling flags from memory.
My write-ups for the MobileHackingLabs iOS challenges: reverse engineering the apps, hooking with Frida, bypassing anti-debug and jailbreak checks, and pulling flags from memory.
How I chained two logic flaws in a crypto P2P platform — frontend-only 2FA and poor session isolation — to add a payout method to a victim's account and sell their USDT without ever passing OTP.
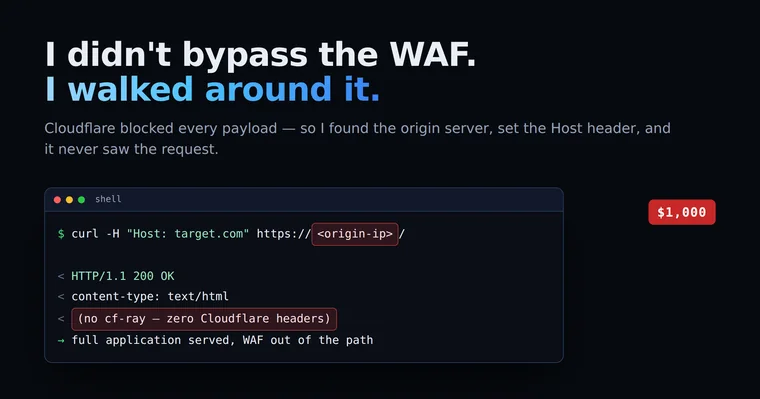
How I bypassed Cloudflare WAF protection by finding the origin IP and modifying the HOST header — a simple trick that earned a $1000 bounty.
Discovering two Remote Code Execution vulnerabilities in a bug bounty program using Shodan recon and default SAP Commerce credentials.
Penetration Tester with 500+ vulnerabilities reported across HackerOne, Bugcrowd, HackenProof and Immunefi. Responsibly disclosed issues to Binance, Oracle, VMware, Huawei and John Deere. Specialized in web, API and mobile application security, with a strong focus on business logic flaws, authorization and authentication bypasses, IDORs and API abuse. Also experienced in Active Directory penetration testing and source code review.
Bug bounty tips and field notes, posted as I find them — follow on X
Bug Bounty Program swag for responsible disclosure
Acknowledged in Oracle's Critical Patch Update — On-Line Presence Security Contributors
Ranked #31 Worldwide on the 2025 leaderboard
Top 3 Researcher in Binance Bug Bounty Program
Two official acknowledgment letters for accepted vulnerability reports
Official swag for responsible disclosure of a security issue
1 CVE Discovered and Counting...
Fetches, downloads, and decompiles Android/iOS/exe assets from HackerOne bug bounty programs.
Burp Suite extension that automates session token swapping across Burp tabs during security testing.
Self-hosted bot that watches HackerOne programs for scope changes and pushes them to Telegram, 24/7.
Mobile Application Penetration Tester
INE Security
Web Application Penetration Tester eXtreme
INE Security
Certified Professional Penetration Tester
INE Security
Offensive Security Certified Professional
OffSec
$ ssh 0xbartita@connect
Connecting to 0xbartita...
Connection established.
$ cat contact_info.txt
a_7_m_e_d_
github.com/0xbartita
linkedin.com/in/0xbartita
x.com/0xbartita
$ _